Sign in and secure your account
Sign in
Section titled “Sign in”-
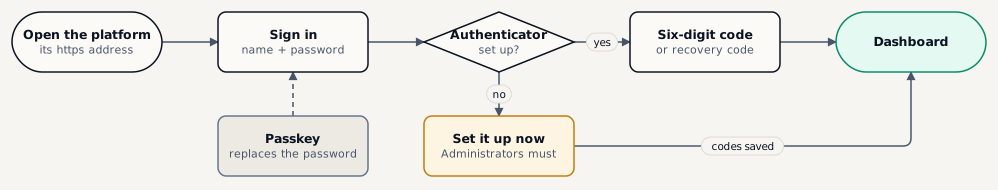
Open the platform’s address in your browser
You land on Sign in. Tick Keep me signed in only on a computer you trust.
-
Enter your user name and password, then Sign in
If your browser has a passkey for this account, Sign in with a passkey does the same in one step.
-
Enter the six-digit code from your authenticator
Lost the phone? Choose Use a recovery code instead and type one of your saved codes. Each code works once.
Set up the second factor
Section titled “Set up the second factor”Administrators must have a second factor: on their first sign-in the platform asks for it before anything else. Everyone else can add one at any time from the account menu.
-
Open the account menu (top right) › Account security
-
Scan the QR code with an authenticator app
Microsoft Authenticator, Google Authenticator, 1Password, Bitwarden and similar apps all work. No camera? Type the key shown under the code.
-
Enter the six digits the app shows, then Turn on two-factor sign-in
-
Save the 10 recovery codes
They are shown once. Store them away from your password - a password manager or a printed copy in a safe place.
Confirm it is you
Section titled “Confirm it is you”Sensitive actions ask for a fresh authenticator code first (step-up): pinning a host key, rotating a credential, approving a restore, managing storage, keys, environments, users or API tokens, and exporting the recovery kit. One code unlocks them for 5 minutes. Recovery codes are not accepted here.
Good to know
Section titled “Good to know”| Rule | Default |
|---|---|
| Idle session ends after | 30 minutes without activity |
| Any session ends after | 12 hours, active or not |
| Account locks after | 5 wrong passwords within 15 minutes, for 15 minutes |
| Recovery codes | 10, each used once |
The very first administrator
Section titled “The very first administrator”A new platform has no account. Whoever installs it opens /Account/Setup and pastes the setup token the platform printed in its log when it started, with the new administrator’s name, e-mail and password. Once an account exists, that page is gone for good.